Many AFSL and ACL licensees have the components of compliance infrastructure. They have policies, registers, committees, monitoring programs and reporting packs. The weakness is often not the absence of these elements, but the lack of a clear operating model connecting them.
An obligation may have a nominated owner, but no defined workflow. A workflow may generate tasks, but no reliable evidence. An issue may be escalated, but the decision and rationale are not preserved. A report may show completed activity, but not whether the underlying control is effective.
The result is a collection of compliance processes rather than a compliance operating system.
A workable operating model establishes how responsibility moves through the organisation and how evidence moves with it.
Ownership is not the same as accountability
Ownership identifies who is responsible for maintaining an obligation, control or process.
Accountability identifies who must answer for the outcome.
The distinction matters because compliance responsibilities are often distributed. A business leader may own a process. A compliance team may advise or monitor it. A Responsible Manager may oversee a regulated function. A board may retain ultimate governance responsibility.
When these roles are blurred, operational work is delayed and difficult decisions are pushed between teams. Business owners may assume compliance is responsible for implementation. Compliance may identify issues without having authority to require action. Responsible Managers may receive information without a clear escalation path.
A sound operating model defines who performs the work, who approves key decisions, who monitors the outcome and who must be informed when risk changes.
Workflow turns responsibility into action
A role description or responsibility matrix does not ensure that an obligation is being managed.
Responsibility becomes operational through workflow.
A workflow should identify the trigger, required activity, decision points, evidence, timeframes, escalation thresholds and closure conditions. It should also show what happens when the normal process fails.
For example, assigning ownership of complaint management is not enough. The operating model must address intake, classification, investigation, customer response, potential breach assessment, root-cause analysis, remediation and reporting.
Each stage should produce evidence that can be connected to the original complaint and the obligations or controls it may affect.
Without this structure, similar matters can be handled differently, important decisions may go undocumented and recurring issues can remain hidden across separate records.
Escalation must support judgement
Escalation is sometimes treated as a notification step. In practice, it is a governance mechanism.
A good escalation process identifies when an issue requires a different level of authority, expertise or scrutiny. It should direct matters to people capable of making the necessary judgement and provide them with the evidence required to do so.
Escalation thresholds may relate to customer harm, potential reportability, repeated control failure, financial exposure, systemic impact or overdue remediation.
The operating model must also record what happened after escalation. A notification without a decision trail does not show how the issue was governed.
Reporting should follow risk, not organisational structure
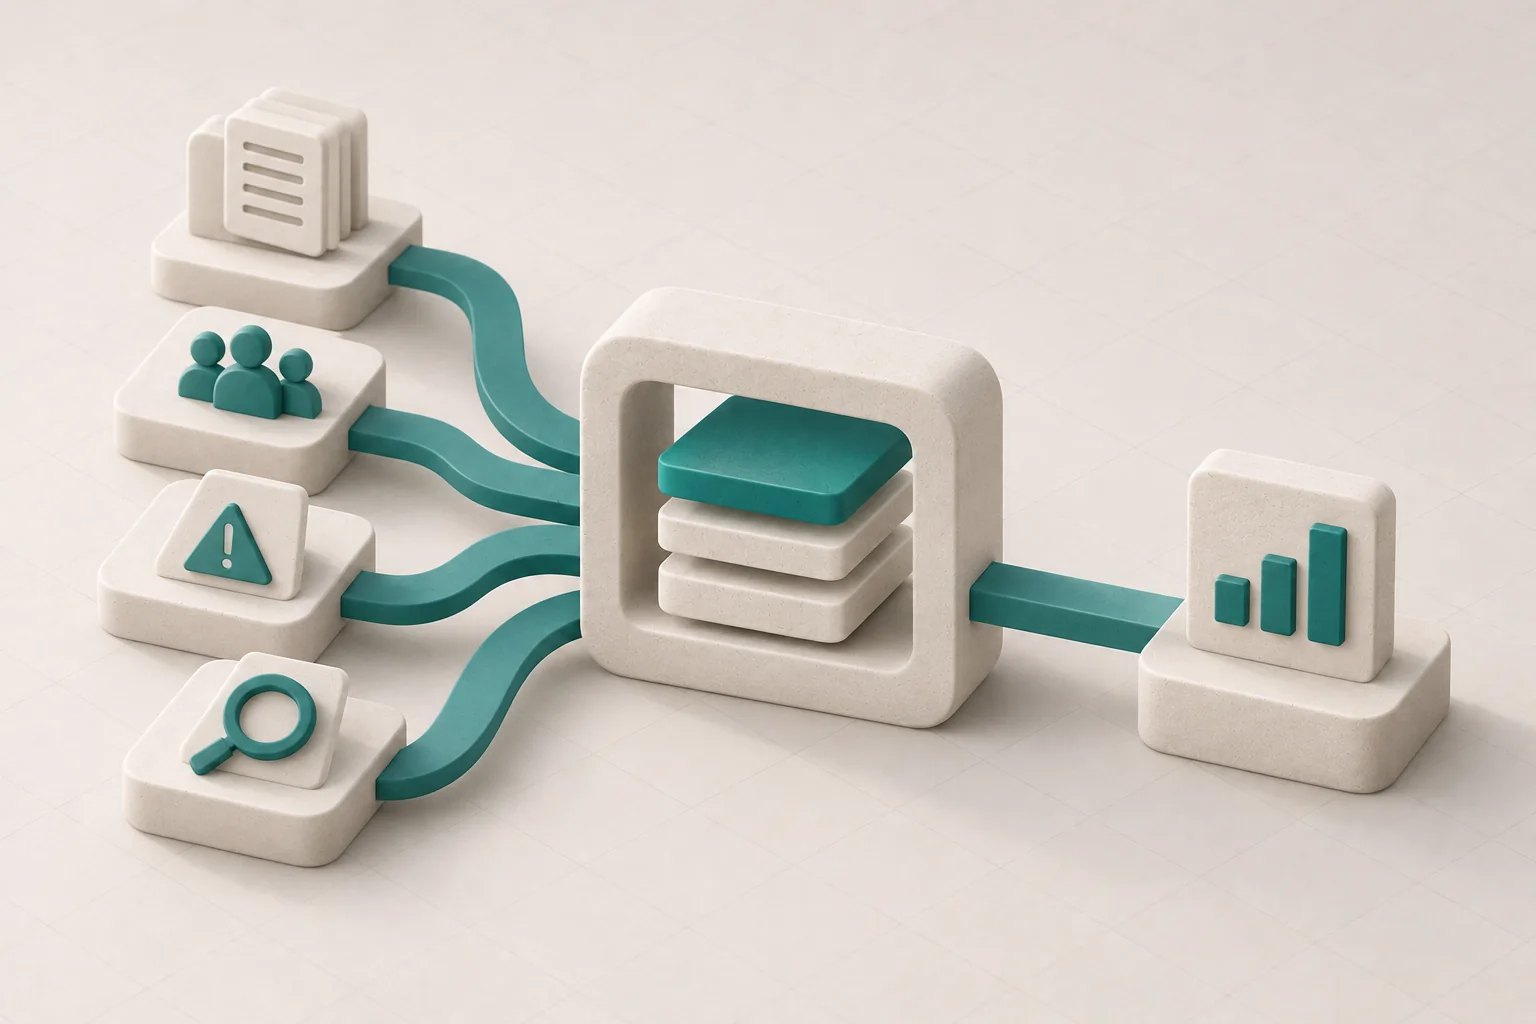
Compliance reporting often mirrors separate registers and team responsibilities. Complaints are reported in one section, incidents in another, monitoring findings elsewhere and remediation in a separate action log.
This can conceal relationships between them.
Effective reporting connects information around the obligation, control or risk. It distinguishes routine activity from exceptions, emerging themes and unresolved exposure. It also explains whether management action is reducing the risk.
Boards and Responsible Managers need more than counts of reviews, training completions or closed actions. They need governance intelligence that directs attention to matters requiring challenge or decision.
Assurance and review complete the model
Assurance tests whether the operating model is producing the intended result.
It asks whether controls are appropriately designed, whether workflows are being followed, whether evidence is reliable and whether remediation has been effective. It also tests whether governance reporting reflects the real condition of the business.
Review then uses those findings to improve the model.
This is not limited to an annual policy review. It includes reconsidering ownership, thresholds, workflows, reporting and control design when the business, regulatory environment or risk profile changes.
An operating model that is not reviewed eventually becomes a description of how the organisation used to work.
What this means in practice
A licensee should be able to show:
- Who owns each material obligation and who is accountable for the outcome.
- Which workflow gives practical effect to that responsibility.
- When issues must be escalated and who has authority to decide.
- How evidence moves from activity into risk-weighted governance reporting.
- How assurance and review improve the model over time.
How [complyᵉ] supports this
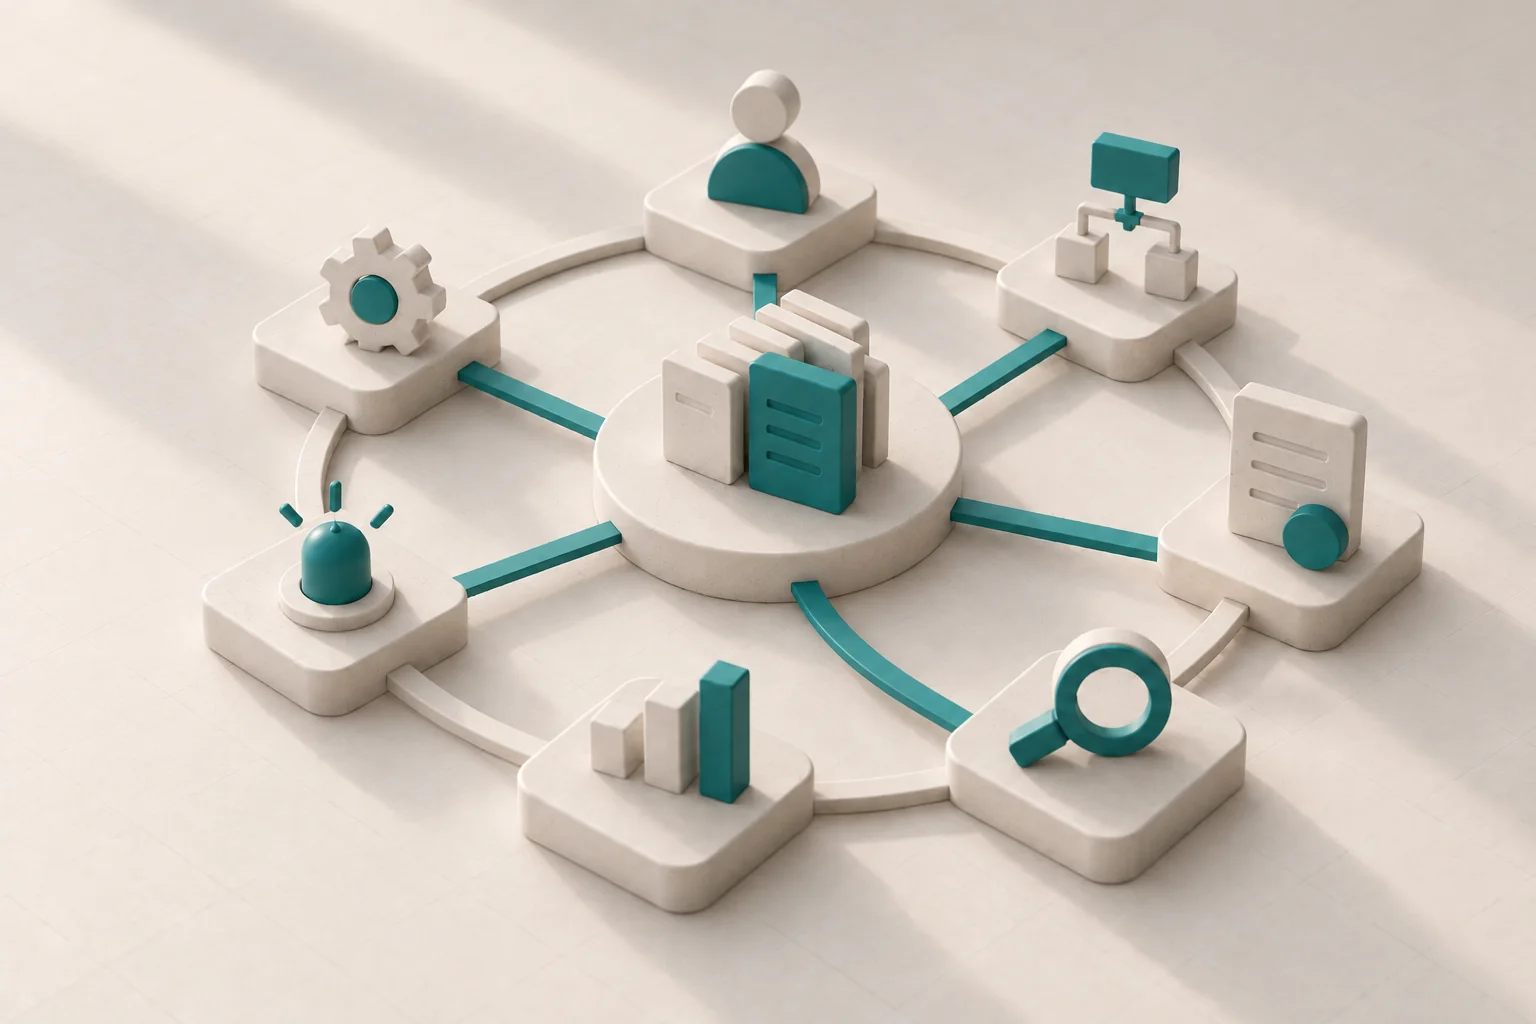
[complyᵉ] helps licensees structure ownership, workflows, escalation, evidence, remediation and reporting within a connected compliance operating system.
It supports clearer decision trails, more consistent execution and better visibility across related compliance activities. This allows assurance findings, incidents, complaints and remedial actions to inform governance rather than remain isolated in separate registers.
Technology does not replace legal analysis, professional judgement or board accountability. It provides the structure needed for those functions to operate with better evidence and clearer oversight.
A compliance operating model works when responsibility is visible, activity is controlled and evidence reaches the people required to act on it.