AFSL and ACL licensees rarely lack assurance activity.
They conduct file reviews, monitor advisers, supervise representatives, investigate complaints and breaches, respond to AFCA matters, complete audits and review surveillance findings. ASIC correspondence may generate further actions, reviews or reporting.
The problem is that these activities are often managed separately.
Each team has its own register, methodology, reporting cycle and definition of significance. File review findings remain within advice monitoring. Complaints are analysed by customer operations. Breach investigations sit with compliance. Audit findings are tracked in another system. AFCA outcomes are treated as individual disputes. ASIC matters are reported through separate governance channels.
This creates multiple views of the same organisation, but no single governance picture.
Assurance sources are different, but the risks may be the same
Each assurance source serves a distinct purpose.
File reviews test the quality of advice or other regulated activity against expected standards.
Complaints show where customers have experienced dissatisfaction, confusion, delay, loss or poor outcomes.
Breach investigations examine potential failures to meet legal and regulatory obligations.
Audit provides structured and, where appropriately independent, validation of controls and governance arrangements.
Supervision and surveillance observe conduct, behaviour and emerging risks closer to the point of activity.
AFCA matters provide external evidence about customer disputes, recurring weaknesses and the adequacy of internal responses.
ASIC engagement may identify concerns about governance, conduct, reporting, systems or organisational capability.
Adviser monitoring tracks individual and cohort-level patterns across files, conduct indicators, complaints, training and remediation.
These sources should not be collapsed into a single undifferentiated dataset. Their evidentiary weight, purpose and limitations differ.
They should, however, be connected.
A complaint, an AFCA determination, a failed file review and a breach investigation may all point to the same advice process, product, representative cohort or supervision weakness. When each matter is assessed independently, the organisation may see isolated incidents. When the evidence is considered together, it may reveal a recurring control failure.
That is the purpose of integrated assurance.
Integration requires a common risk structure
An integrated assurance framework does not begin with a consolidated report.
It begins with a common structure for classifying evidence.
Assurance findings should be capable of being linked to the relevant obligation, control, product, service, representative, customer outcome, business process and remediation action. This creates a shared reference point across different assurance activities.
Without that structure, comparisons remain subjective.
A complaint may be categorised by issue type. A file review may be coded by advice standard. An audit finding may be recorded against a control. A breach investigation may refer to a statutory obligation. Unless those records can be connected, the organisation cannot readily determine whether they describe the same underlying risk.
A common structure also improves escalation. The significance of a single finding may be limited. Its significance changes when the same issue appears across multiple assurance sources.
Reporting should move beyond volumes
Integrated assurance is not achieved by placing several graphs on the same dashboard.
A board does not gain a coherent view merely because it receives the number of complaints, file reviews, breaches, AFCA matters and audit actions in one paper.
Volumes describe activity. Governance requires interpretation.
An effective assurance picture should explain where evidence converges, where it conflicts and where uncertainty remains. It should identify recurring failures, control weaknesses, affected customer groups, overdue remediation and areas where management conclusions require challenge.
It should also distinguish between leading and lagging indicators.
Surveillance findings, supervision concerns and adviser monitoring trends may provide early warning. Complaints, AFCA matters and breach outcomes may confirm that harm has occurred. Audit may test whether the response and control environment are adequate.
Viewed together, these signals support more timely and proportionate decisions.
Integrated assurance strengthens remediation
Fragmented assurance often produces fragmented remediation.
A complaint leads to a customer response. A file review leads to adviser coaching. An audit finding leads to a control action. A breach investigation leads to a separate remediation plan.
Each response may be reasonable, but the organisation can still miss the shared root cause.
Integrated assurance connects findings before remediation is designed. It allows management to determine whether the problem is individual, procedural, systemic or cultural.
It also strengthens effectiveness testing. A remediation action should not be considered successful merely because the task was completed. Subsequent file reviews, complaints, surveillance results, AFCA matters and adviser monitoring should provide evidence about whether the underlying risk has reduced.
What this means in practice
Licensees should ask:
- Can assurance findings be linked to common obligations, controls and risks?
- Can related signals across file reviews, complaints, breaches, audit and external matters be identified?
- Does escalation reflect the combined significance of multiple findings?
- Does reporting explain themes and control implications rather than only volumes?
- Is remediation effectiveness tested across the assurance sources that first identified the problem?
How [complyᵉ] supports this
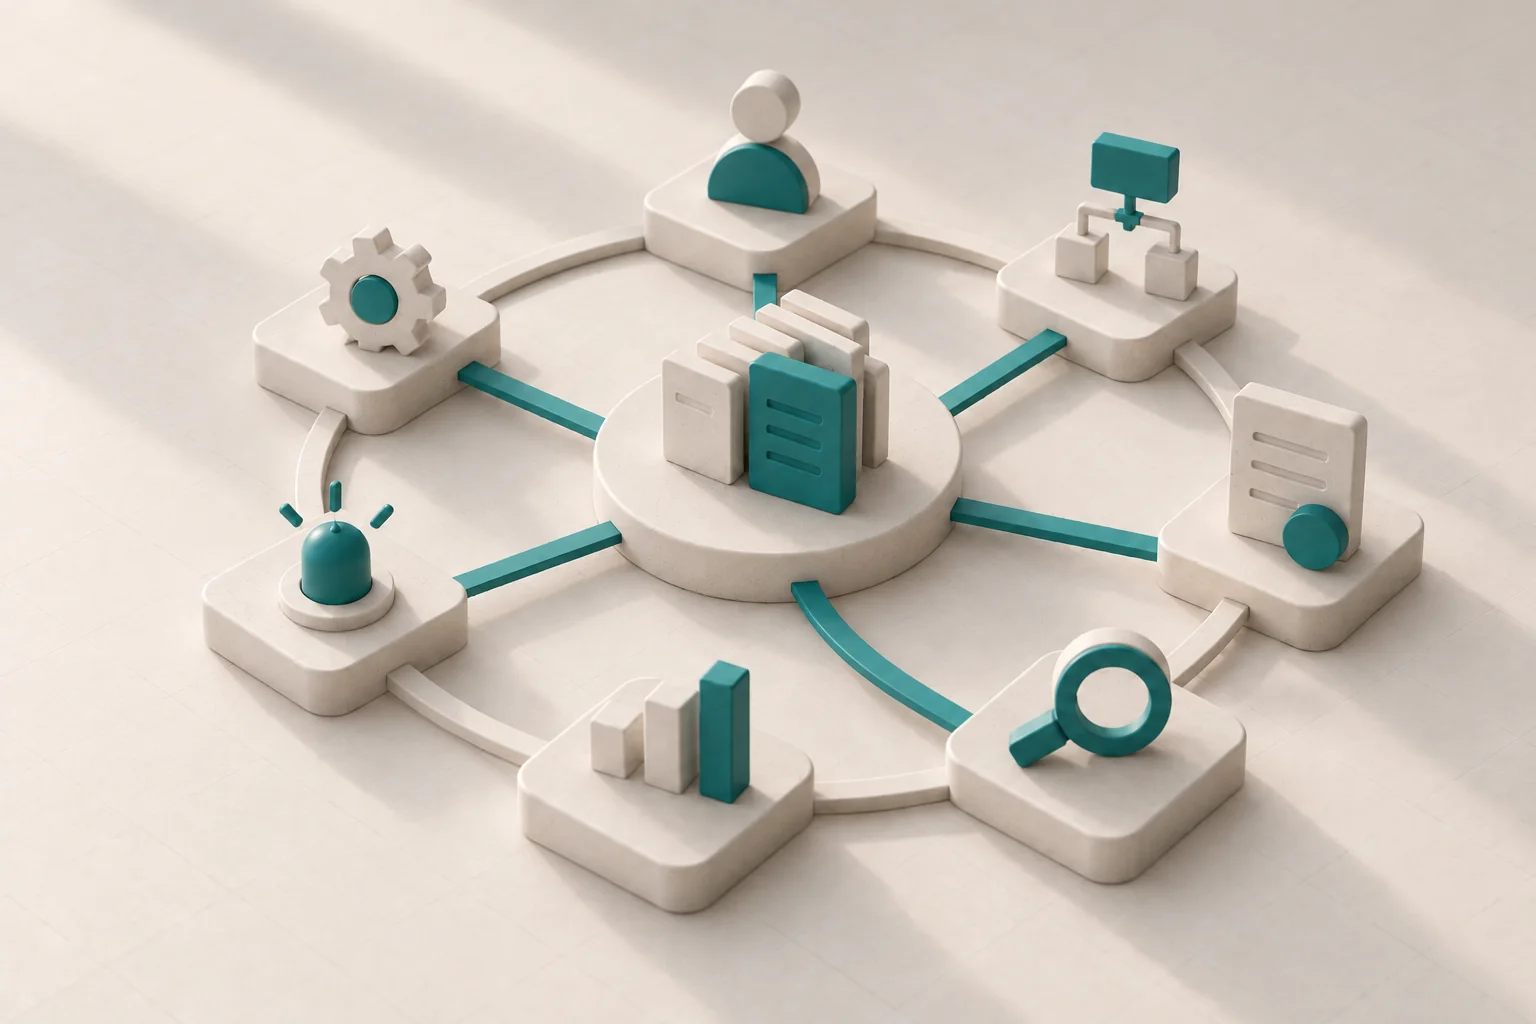
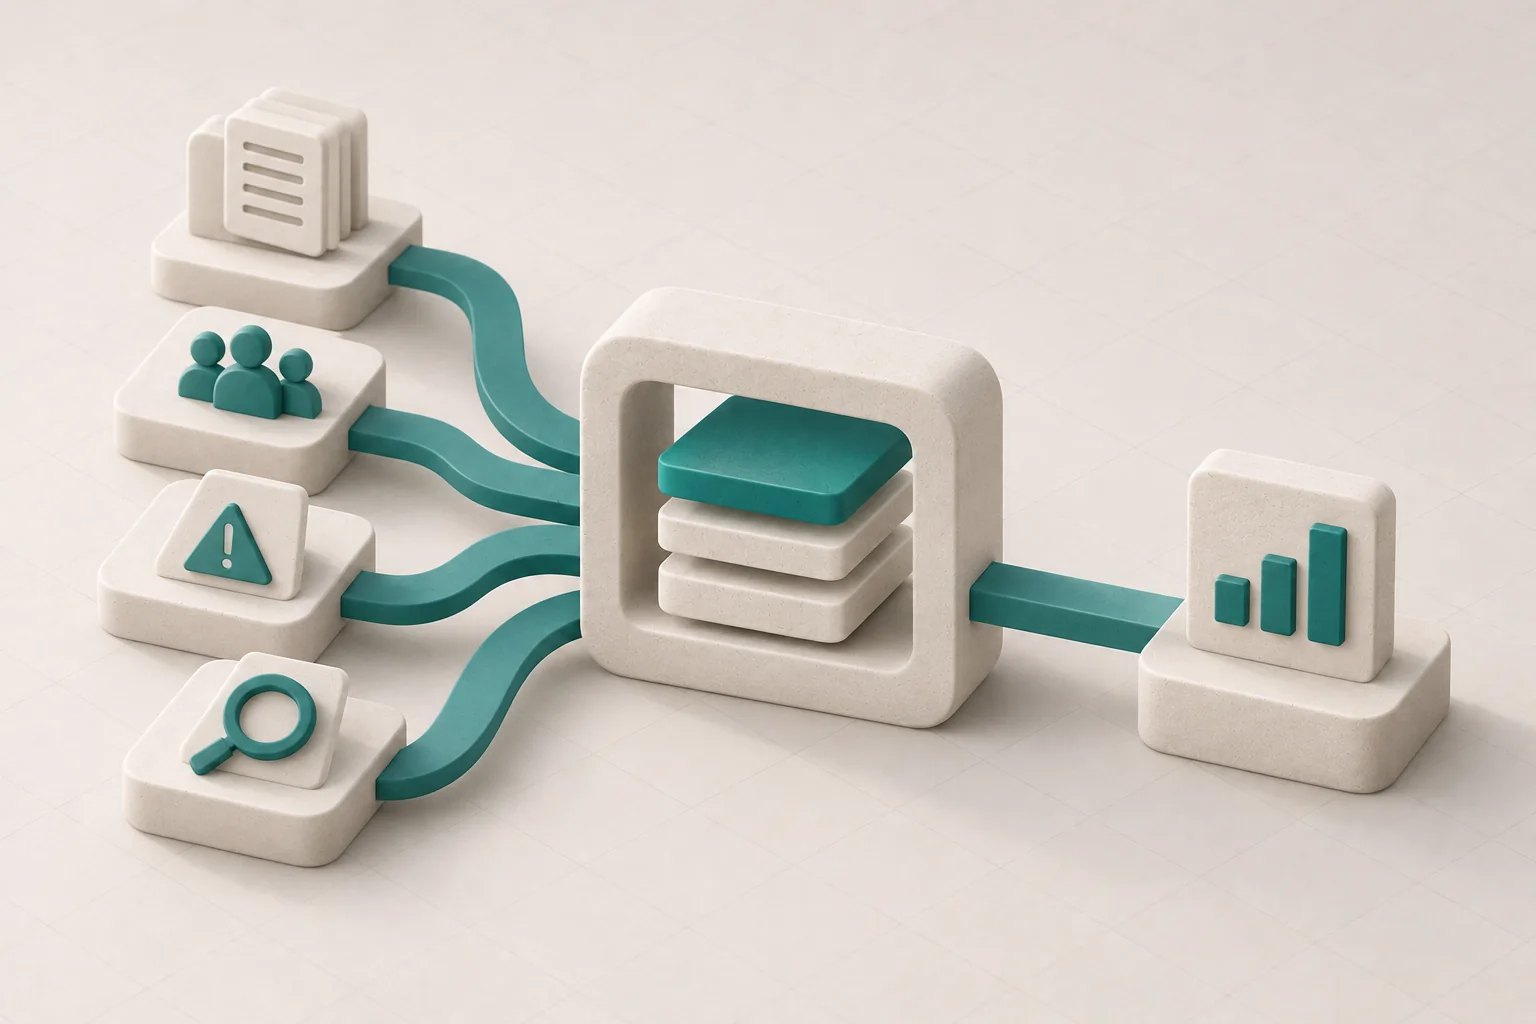
[complyᵉ] helps licensees connect file reviews, complaints, breaches, audit, supervision, surveillance, AFCA matters, ASIC engagement and adviser monitoring within a shared governance structure.
It supports consistent classification, connected evidence, defensible decision trails and coordinated remediation. It also helps Responsible Managers and boards see where separate findings point to a common risk or control weakness.
Technology does not replace independent assurance, legal analysis or professional judgement. It makes the relationships between different sources of evidence more visible and usable.
Integrated assurance does not mean doing more reviews. It means using existing assurance activity to form better governance conclusions.